NCP Secure Enterprise Solution—Centrally Managed Enterprise VPN for Secure Remote Access
NCP Secure Enterprise Solution combines secure remote access, centralized administration, and a straightforward user experience in one modular platform. Designed for large and distributed environments, it enables organizations to securely connect and centrally manage remote users across different locations and supported devices.
With more than 40 years of experience in secure remote access, NCP technology is used by more than 35,000 customers worldwide.
NCP Secure Enterprise Clients NCP Secure Enterprise Management NCP Secure Enterprise Server
What is NCP Secure Enterprise Solution?
Organizations need to provide employees with secure access to corporate applications, systems, and data — regardless of where they are working, which supported device they use, or which network they connect through. As the number of users, devices, and locations grows, remote access becomes more challenging to secure, scale, and administer efficiently.
NCP Secure Enterprise Solution addresses these requirements through a centrally managed remote-access platform. It allows organizations to provide secure access consistently, enforce security policies centrally, and automate recurring administrative tasks. Its modular, software-based architecture can also be integrated flexibly with existing IT, identity, authentication, and security environments.
NCP Secure Enterprise Solution at a glance
- Suitable for: Companies, public-sector organizations, critical infrastructure operators, and managed service providers
- Use cases: Centrally managed secure remote access for large, distributed infrastructures
- Scalability: From 100 to more than 100,000 users
- Operating systems: Windows, macOS, Linux
- Security: IPsec VPN, multi-factor authentication, and support for Zero Trust strategies
- Administration: Centrally through NCP Secure Enterprise Management
How does NCP Secure Enterprise Solution work?
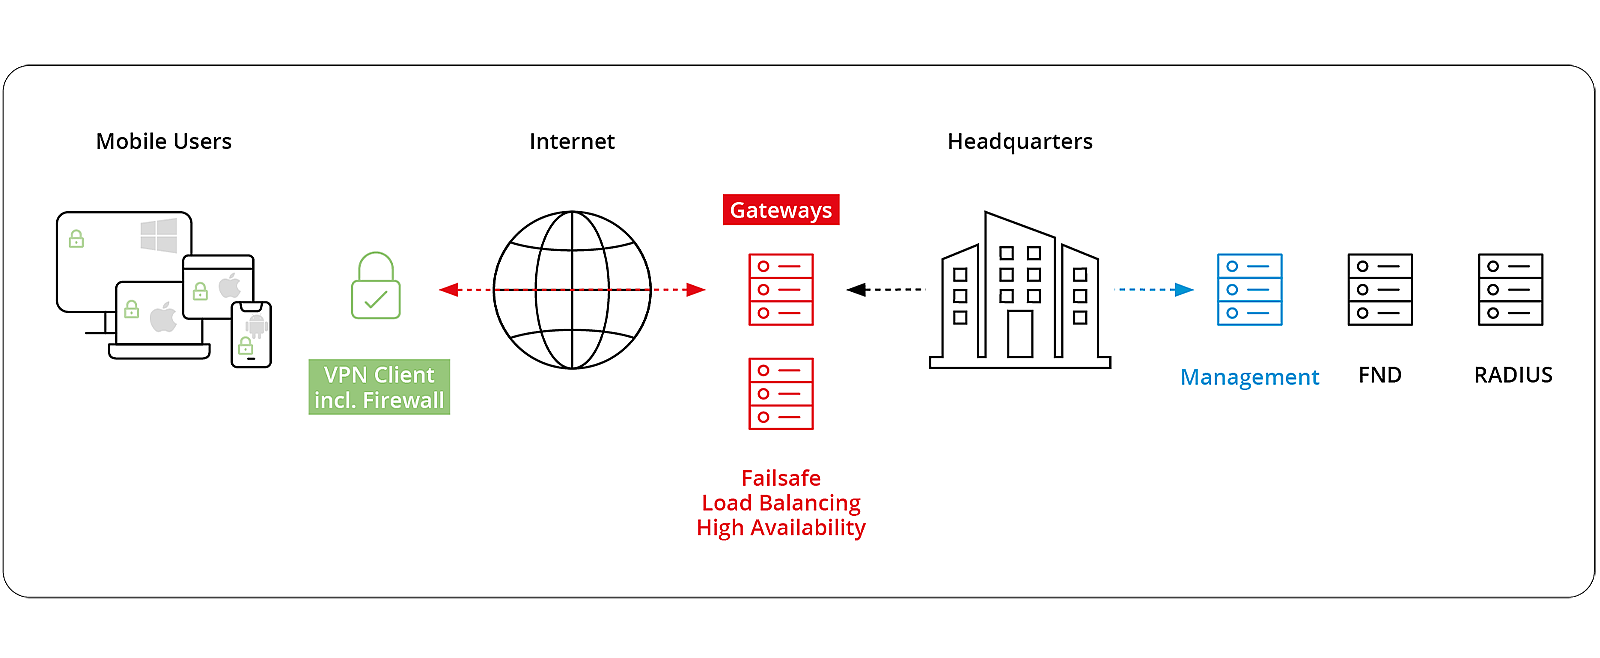
NCP Secure Enterprise Solution consists of three closely integrated components:
The NCP Secure Enterprise Client establishes secure connections between the device and the corporate network. It also applies centrally defined security and connection policies on the end device.
The NCP Secure Enterprise Management allows IT administrators to manage users, configurations, certificates, security policies, licenses, and updates. It also automates recurring administrative processes.
The NCP Secure Enterprise VPN Server acts as the central gateway for incoming connections. It authenticates users and end devices, establishes encrypted VPN tunnels, and controls secure access to authorized corporate resources.
Together, these three components provide a centrally managed remote-access infrastructure that can be operated securely and scaled as your organization grows.
Built to support your Zero Trust strategy
NCP Secure Enterprise Solution provides secure remote access and can form part of a broader Zero Trust architecture. Centralized security policies, strong authentication, secure identities, and endpoint security checks help organizations control access to corporate resources more precisely. Its modular architecture allows the solution to integrate with existing IT and security infrastructures while providing the secure connectivity and centralized controls required as part of a broader Zero Trust strategy.
Why choose NCP?
Thousands of organizations worldwide rely on NCP for secure remote access.

More than 40 years of remote-access expertise
NCP has more than four decades of experience in remote-access technology and serves over 35,000 customers worldwide.

Security Made in Germany
Our products are developed in Germany to meet demanding security requirements, including those of public-sector organizations and other security-sensitive environments.

Proprietary technology & expert support
Our solutions include proprietary features such as the patented NCP Path Finder Technology.

Flexible integration & scalability
NCP products are fully software-based, vendor-independent, and designed to integrate with existing IT infrastructures. The modular architecture supports deployments ranging from several hundred to well over 100,000 users.
The Next Steps
Are you interested in centrally managing your remote access workstations and simplifying administrative processes?
We provide expert advice and support during the planning phase, along with tailored assistance when integrating the solution into your existing infrastructure. Our team offers technical support throughout the entire process, right up to the full deployment of your NCP Enterprise VPN environment.
Frequently asked questions
Find key information about the NCP Secure Enterprise Solution at a glance.
VPN technology can be used for several different purposes. Consumer VPN services are primarily designed for individuals. They typically encrypt a user’s internet connection when browsing on public networks or allow the user to connect through an IP address in another location.
A business or enterprise VPN serves a different purpose: It gives employees secure access to internal corporate resources such as applications, servers, and data, whether they are working from home, traveling, or based at another company location.
An enterprise VPN is also designed to support large, distributed remote-access environments. IT administrators can centrally manage VPN clients, users, security policies, certificates, licenses, and software updates while automating recurring administrative processes. This makes it possible to manage hundreds or thousands of remote-access users securely and efficiently.
| Entry-level VPN | Enterprise VPN |
|---|---|
| Designed for individual workstations and smaller installations | Designed for large, distributed remote-access infrastructures |
| Supports up to 100 users | Supports between 100 and more than 100,000 users |
| Clients are managed individually | Clients are managed centrally |
| Configuration is primarily manual | Configurations can be managed and distributed centrally |
| Suitable for straightforward VPN environments | Suitable for global deployments and ongoing management |
NCP Secure Entry Clients are primarily designed for individual workstations and smaller installations with up to 100 users. NCP Secure Enterprise Solution is designed for larger deployments, site-to-site connectivity, and environments with more than 100 users.
It can also be incorporated into cloud-based security environments and modern Zero Trust architectures. Depending on the deployment, NCP solutions can integrate with technologies and standards such as SASE, SD-WAN, SSE, and SSO via SAML. Standards-based IPsec also allows NCP clients to work with a wide range of compatible third-party VPN gateways.
An enterprise VPN gives employees secure access to corporate resources through encrypted VPN connections, whether they are working from home, traveling, or based at another location.
NCP Secure Enterprise Solution combines centrally managed VPN clients, centralized administration, and powerful VPN gateways. This allows organizations to provide secure connections while managing and automating even large remote-access infrastructures from a central platform.
NCP Secure Enterprise Solution consists of three coordinated components:
- NCP Secure Enterprise Client: The VPN client establishes a secure connection between the end device and the corporate network. It also applies centrally defined security and connection policies.
- NCP Secure Enterprise Management: The management platform allows IT administrators to manage users, configurations, security policies, certificates, licenses, and updates while automating recurring administrative tasks.
- NCP Secure Enterprise VPN Server: The VPN Server serves as the central gateway for VPN connections, authenticates incoming connections, and provides encrypted VPN tunnels to the corporate network.
Together, these components form a centrally managed, secure, and scalable remote-access infrastructure.Zu den zentralen Funktionen gehören unter anderem Path Finder Technology, Always On VPN, Seamless Roaming, Endpoint Policy Checks, Domain Based Split Tunneling, Personal Firewall, Friendly Net Detection, Secure Hotspot Logon, Home Zone, Mandantenfähigkeit und Windows Pre-Logon.
Welche Funktionen zur Verfügung stehen, hängt von der eingesetzten Komponente und dem Betriebssystem ab. Detaillierte Informationen finden Sie auf den jeweiligen Produktseiten und in den zugehörigen Datenblättern.
Depending on the component and operating system, key features include: Path Finder Technology, Always On VPN, Seamless Roaming, Endpoint Policy Checks, Domain Based Split Tunneling, Personal Firewall, Friendly Net Detection, Secure Hotspot Logon, Home Zone, multi-tenancy, and Windows Pre-Logon.
For detailed information about the available features, see the relevant product pages and data sheets.
| Feature | Benefit |
|---|---|
| NCP Path Finder Technology | Enables VPN access from networks that restrict standard IPsec communication |
| Always-On VPN | Automatically establishes a secure connection |
| Seamless Roaming | Maintains active application sessions when switching between Wi-Fi and cellular networks |
| Endpoint Policy Check | Verify endpoint security requirements before network access is granted |
| Personal Firewall | Provides additional protection for the device |
NCP’s patented Path Finder Technology enables VPN connections in networks where standard IPsec communication is restricted or blocked. When the client detects such a restriction, it can route VPN communication through port 443, which is normally used for HTTPS. The switch occurs automatically and does not require any action from the user. The switch occurs automatically and does not require any action from the user
NCP Secure Enterprise Solution can form part of a broader zero-trust architecture. Centralized security policies, strong authentication, and endpoint security posture checks help organizations control access to corporate resources. The solution can also integrate with existing IT and security systems and broader Zero Trust frameworks.
However, a VPN alone does not constitute a complete Zero Trust strategy. A VPN alone does not provide a complete Zero Trust architecture. However, it can provide the secure connectivity and centralized controls required as part of a wider security strategy.
Implementation time depends on the size and complexity of your existing IT infrastructure and your specific technical, security, and operational requirements. Depending on the project, implementation can take anywhere from a few hours to several weeks. Depending on the project, implementation may take anything from a few hours to several weeks. Our system engineers can support you with planning, integration, deployment, and commissioning.
The required infrastructure depends on your existing IT environment and planned deployment model. NCP Secure Enterprise Solution has a modular, software-based architecture that can be integrated with an existing IT infrastructure. It consists of: NCP Secure Enterprise Clients for end devices, NCP Secure Enterprise Management for centralized administration, and the NCP Secure Enterprise VPN Server as the central VPN gateway. The solution can also integrate with existing identity, authentication, directory, database, and VPN environments.
Do you have questions?
Our team will be happy to advise you personally.
Dombuehler Str. 2, 90449 Nuremberg
+49 911 9968 333
sales@ncp-e.com