The Zero Trust solution for greater security, control, and data sovereignty
Applications, data, and users are increasingly distributed across cloud platforms, data centers, offices, and remote work environments. At the same time, organizations need greater control over who can access individual resources, under which conditions, and from which devices.
Zero Trust addresses this challenge with a simple principle: Never trust, always verify. Instead of granting access based on network location alone, every access request is evaluated against defined security policies before a user can connect to an application or resource.
Secure access without giving up control over your infrastructure and data
NCP combines Zero Trust principles with decades of expertise in secure remote access and VPN technology. This allows organizations to introduce granular, application-level access controls without necessarily replacing their existing secure connectivity infrastructure.
Designed and developed in Germany, NCP solutions give organizations greater control over where security components are operated and how sensitive access and policy decisions are handled.
Whether your environment is cloud-based, on-premise, or hybrid, NCP gives you the flexibility to design a Zero Trust architecture around your operational, security, and data sovereignty requirements.
Three approaches to a modern Zero Trust architecture
Every organization has different requirements for security, infrastructure, regulatory compliance, and data sovereignty. There is therefore no single approach that suits every Zero Trust deployment.
Zero Trust in the cloud
For organizations with cloud-based applications and distributed users
When applications and data are hosted primarily or entirely in the cloud, access can be controlled directly at the application level.
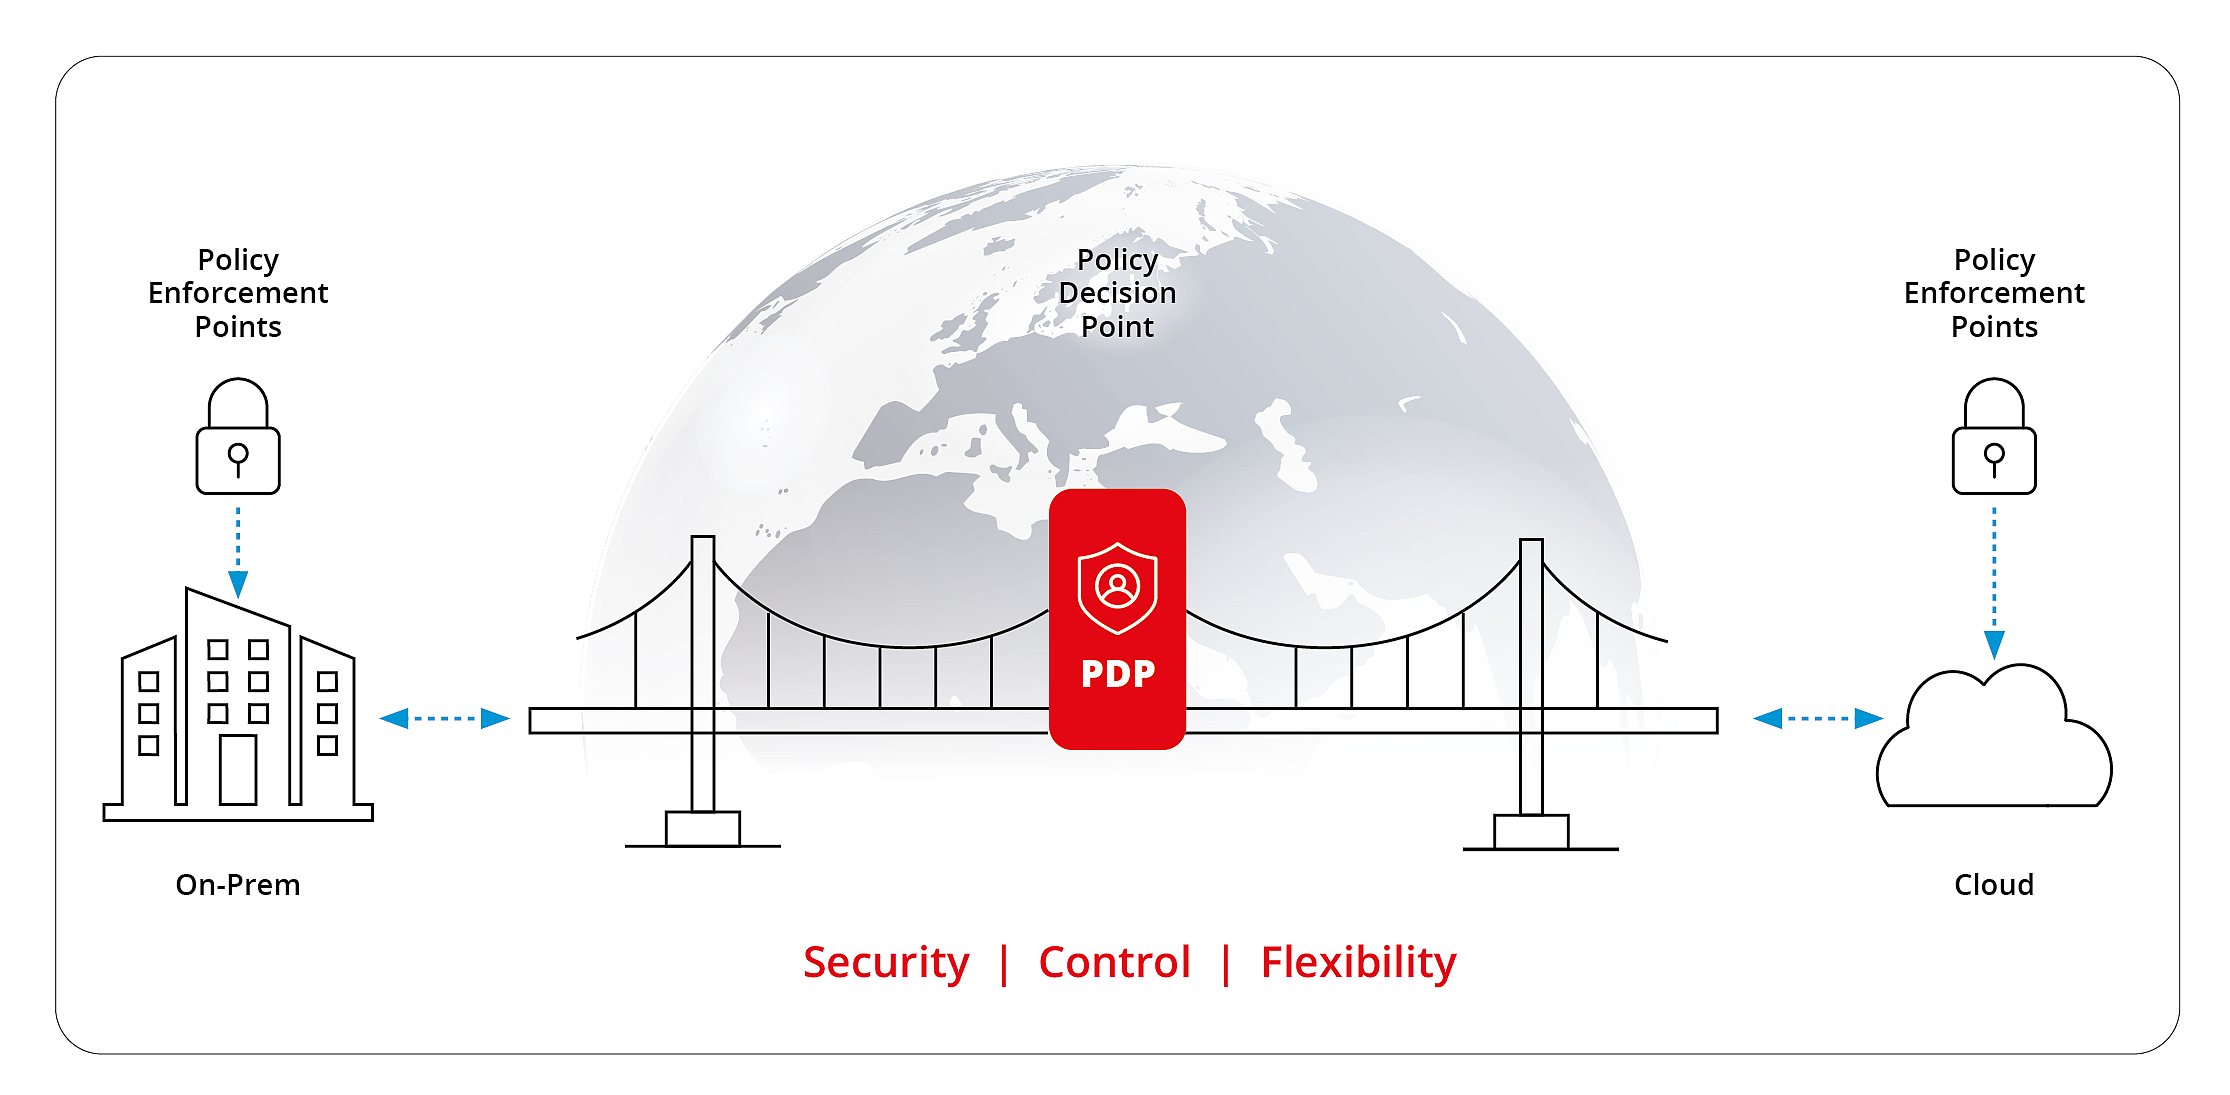
NCP's Policy Decision Point (PDP) can also operate in private cloud environments, enabling organizations to retain control over access decisions within their own infrastructure.
Zero Trust On-Premise
For high-security, regulated, and isolated environments
Not every IT environment can – or should – rely on public cloud services or permanent internet connectivity. Particularly sensitive environments may need to operate entirely offline.
NCP enables on-premises Zero Trust deployments, with the Policy Decision Point operating within the organization's own infrastructure and communicating with Policy Enforcement Points.
Even within a protected internal network, access is never automatically trusted.
Zero Trust in hybrid environments
Combine cloud, on-premises, and existing VPN infrastructure
Many organizations operate hybrid IT environments where cloud applications, on-premises systems and existing VPN infrastructure coexist.
NCP combines Zero Trust with established VPN, IPsec and TLS technologies, allowing organizations to retain existing infrastructure while introducing granular access controls for applications and resources.
Your benefits at a glance
One architecture. Different deployment models. Your control.

100 % "Made in Germany"
Designed and developed in Nuremberg, Germany

Flexible deployment
deploy Zero Trust in cloud, on-premises, or hybrid environments

Data sovereignty
retain control within your own infrastructure or private cloud

Zero Trust and VPN
continue using existing secure remote-access and VPN infrastructure
Frequently asked questions about Zero Trust
Find answers to the most common questions about the Zero Trust concept, its implementation, and practical applications.
IPsec provides secure connections between networks and locations. Individual applications can also be protected through TLS-based connections to Policy Enforcement Points (PEPs). For example, multiple locations can be connected over IPsec while access to individual applications within the infrastructure is controlled according to Zero Trust principles.
This makes it possible to support complex hybrid network structures and scenarios involving technologies such as SD-WAN.
Yes. Zero Trust and VPN technology can be combined effectively.
VPNs remain an important component of modern IT security architectures, particularly for secure network connections, remote access, and site-to-site connectivity. Zero Trust complements the VPN by adding targeted, granular access control for individual applications and resources.
Organizations can therefore continue using their existing VPN infrastructure while implementing Zero Trust controls wherever more differentiated application access is required.
Zero Trust enhances secure remote access — it does not necessarily replace it.
No. NCP Zero Trust does not depend on a public cloud service. Organizations can deploy the relevant components within their own infrastructure or private cloud, depending on their security and operational requirements.
| Scenario | Policy Decision Point (PDP) | Access model |
|---|---|---|
| Cloud | Private cloud | Zero Trust → Application |
| On-premise | Proprietary infrastructure | Zero Trust → Application |
| Hybrid | Private cloud / On-premise | Zero Trust combined with VPN, IPsec, and TLS |
Do you have questions?
Our team will be happy to advise you personally.
Dombuehler Str. 2, 90449 Nuremberg
+49 911 9968 333
sales@ncp-e.com